

I shaped the design and documentation behind AgriWebb's 11-role permissions system, working from a CPO-led customer research process to make sure users could pick the right role without calling support.
with Phil Chan, Dr Kenny Sabir & Alex Trobec
Section 01 – The challenge
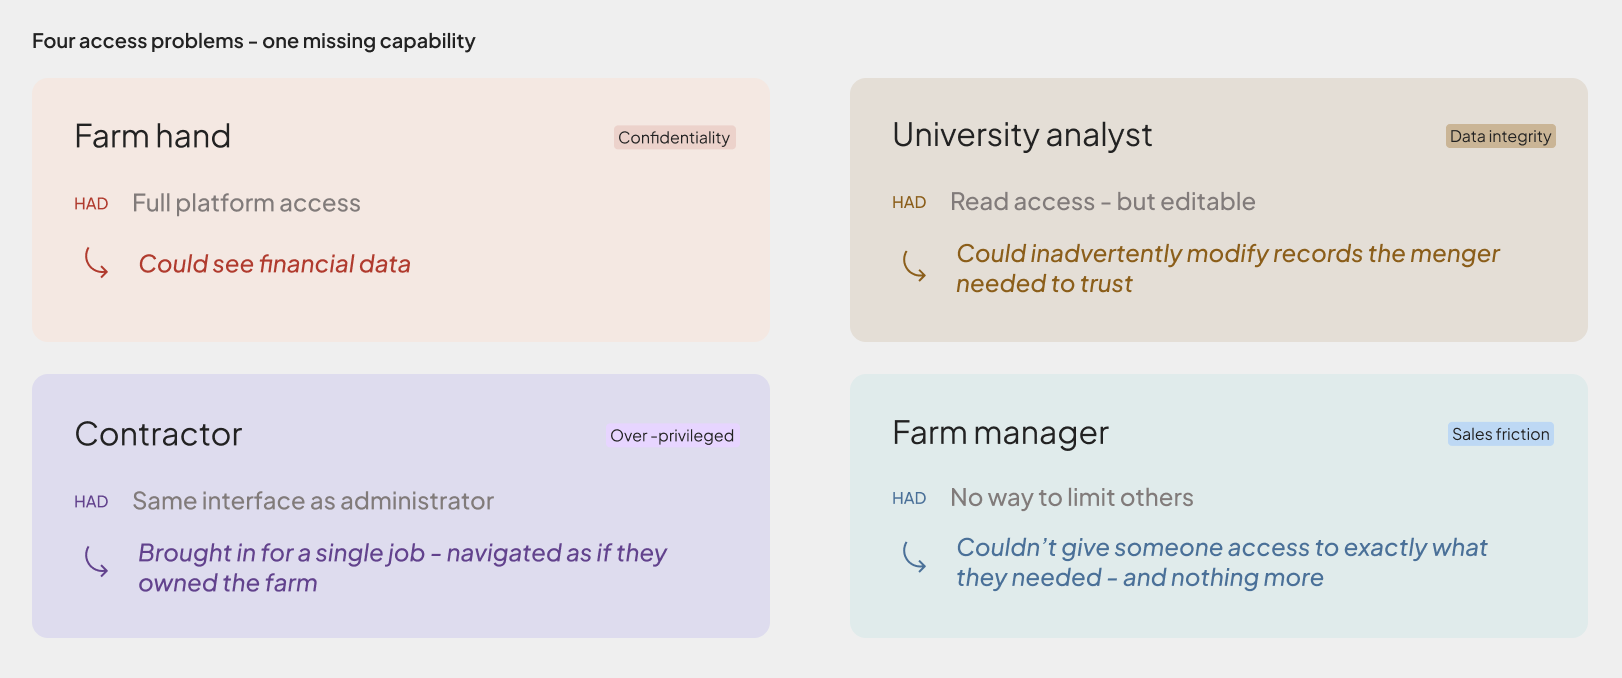
By 2023, AgriWebb’s growth into enterprise multi-farm operations outpaced its basic "Farm user" and "Analyst" roles. Because users had broad platform access, sensitive financials and critical data were exposed to contractors, farm hands, and external analysts alike – hurting sales and swelling support requests. To fix this, AgriWebb needed a flexible, behavior-based role model: granular enough for enterprise security, yet simple enough for farm owners to manage self-service.
Section 02 – The process
"That's our job to make it simple and easy. That's our job, right?"
At AgriWebb, product, design, and development collaborated closely on this project. As a contributor, I helped define the problem, design the interface, and draft documentation.
Scoping & strategy
In a micro-workshop with the CPO and developers, we set goals and intentionally deferred custom roles and granular permissions to keep the initial release focused and shippable.
Core hypothesis
Users should be able to select the correct role independently, guided entirely by the interface without contacting support.
Research & validation
We validated the role taxonomy internally with sales, product, and support, followed by CPO-led interviews with five existing customers.
Key insights
While the role-versus-feature matrix was essential, users found it overwhelming, hard to scan, and unclear regarding post-assignment permissions.
Design execution
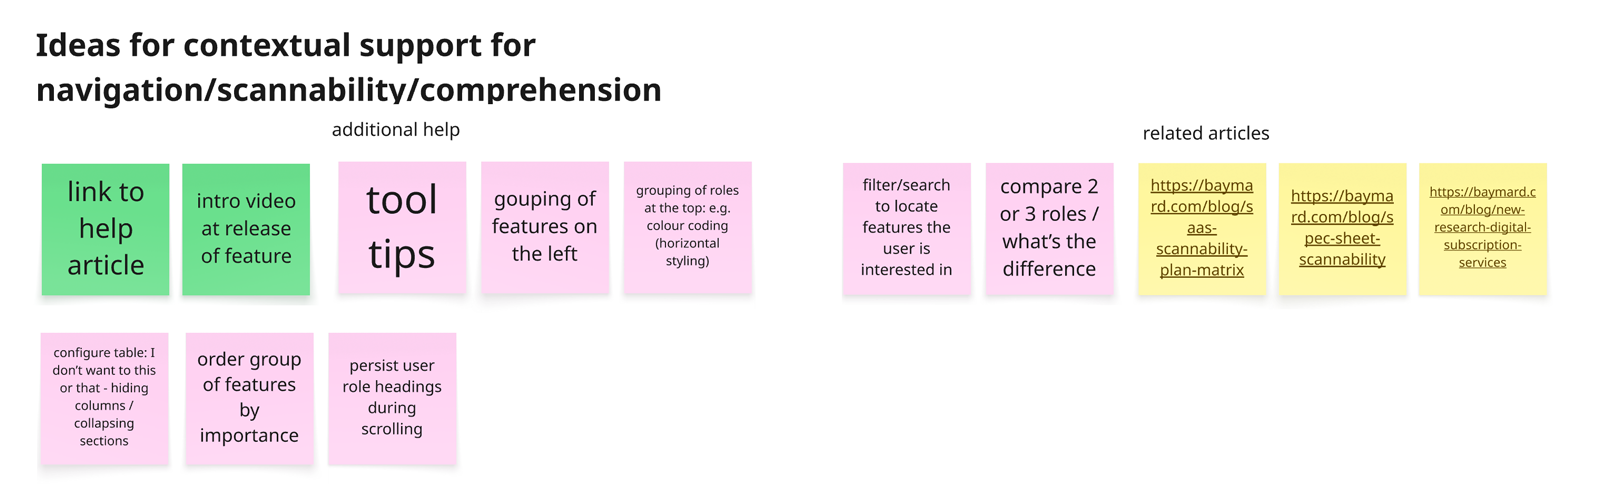
To reduce cognitive load, we explored inline tooltips, feature filtering, role comparisons, sticky headers, color coding, and collapsible sections.
Final solution
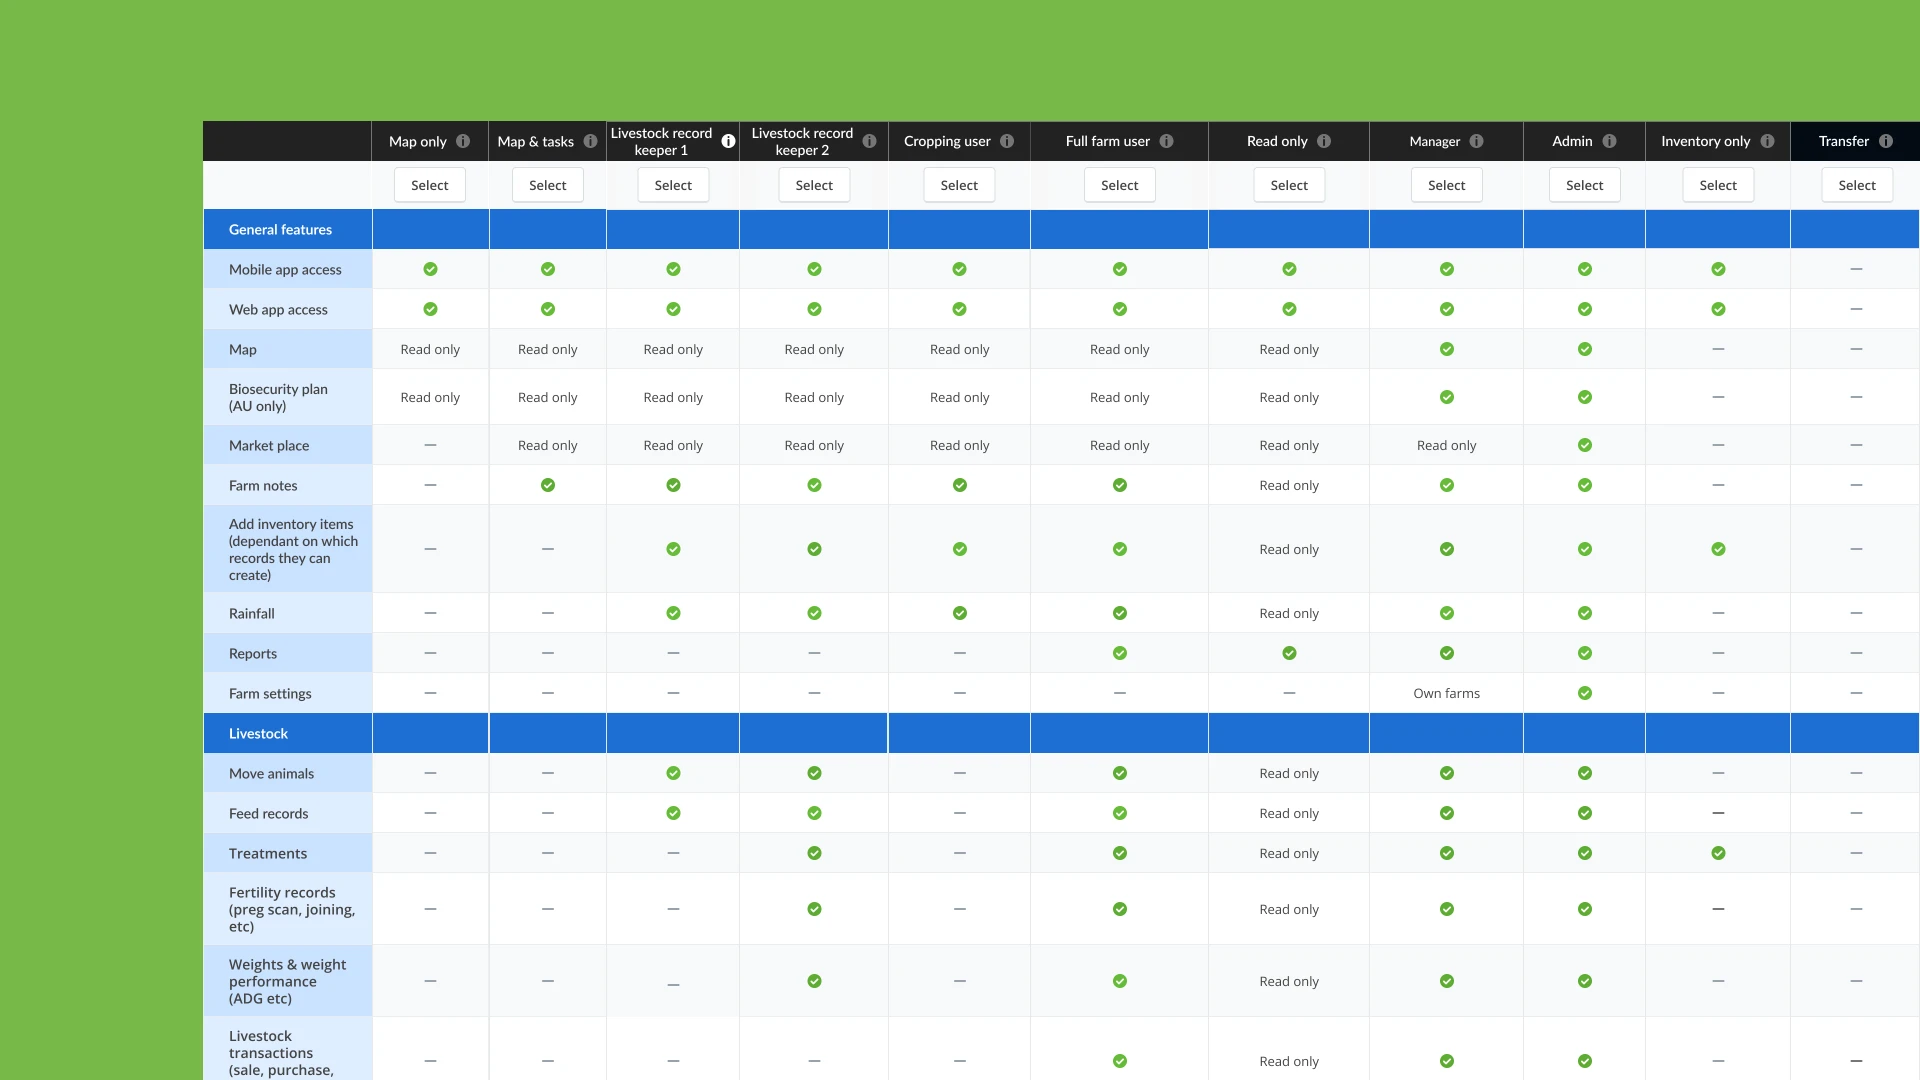
We designed a matrix covering 11 roles across 30+ feature categories (grouped into five core themes). This was launched both in-product and in the AgriWebb Academy as a shared source of truth for customers, sales, and support.
Section 03 – Outcome & impact
- 11
- Roles shipped
- 2
- First phase
- ↓
- Support tickets
- 3
- Items deferred
Full permission model
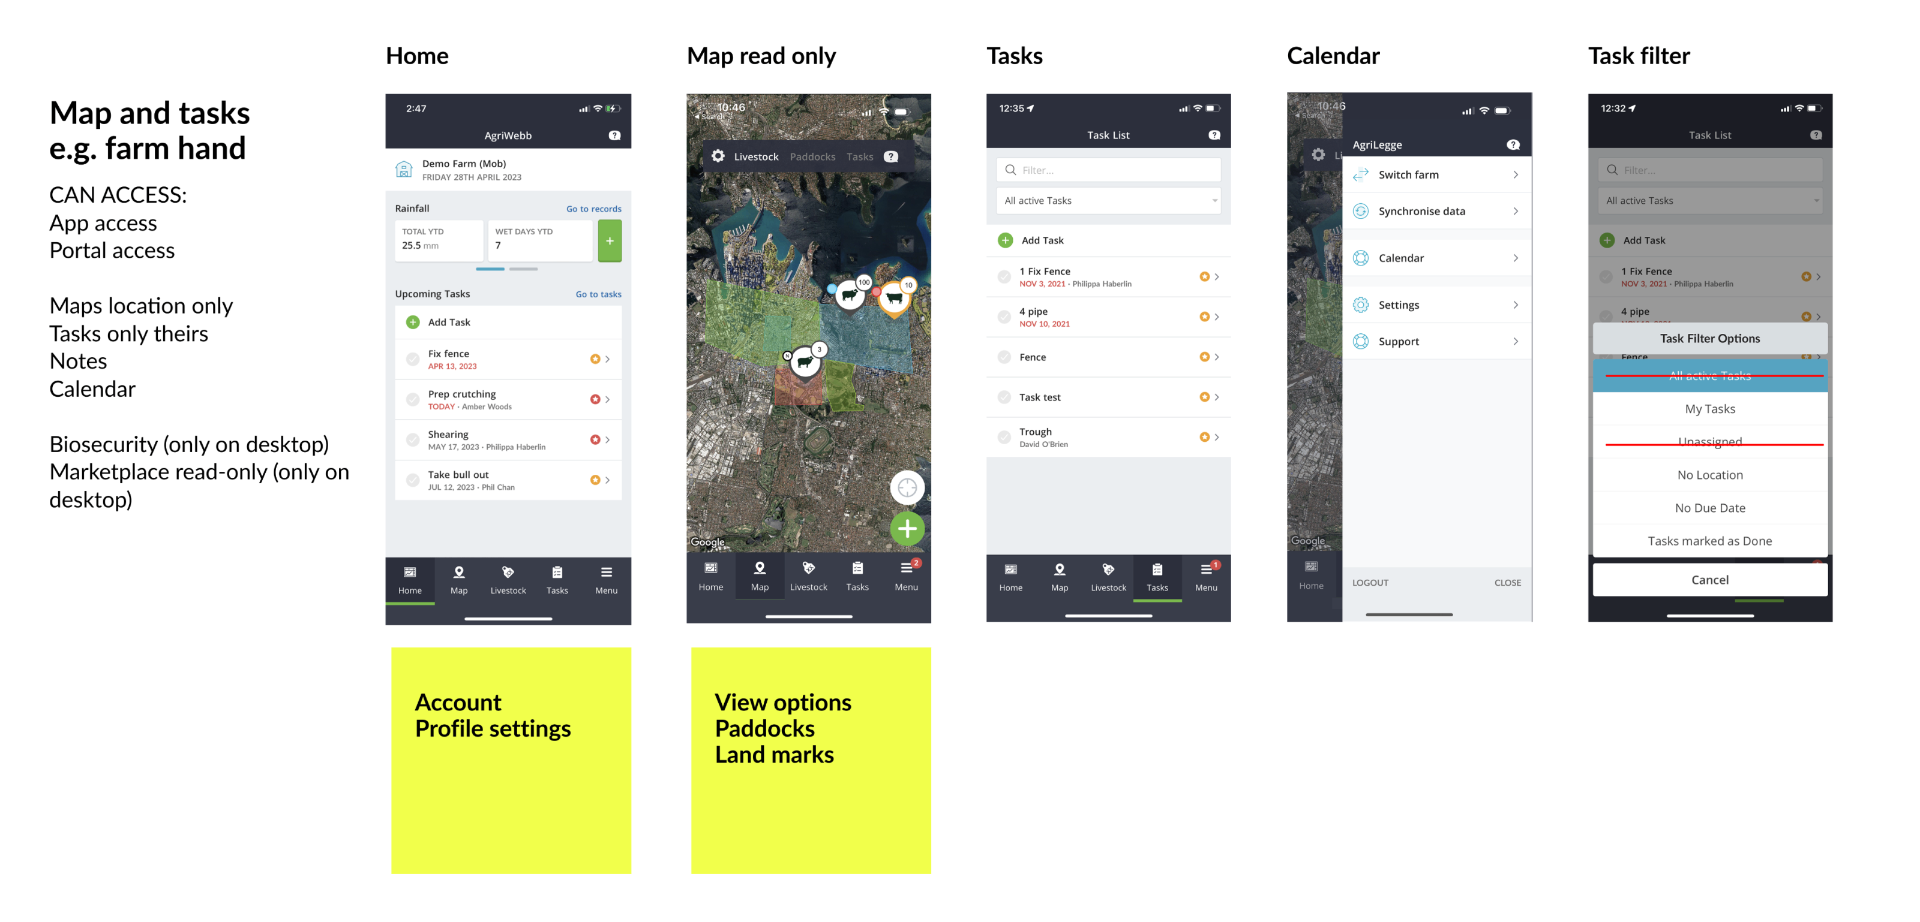
Farm hands + map-only
Post-rollout reduction
Next frontier
The User Roles project was a fascinating UX exercise in radical simplification. The core challenge wasn't just managing permissions, but figuring out how to deliver essential information to the user without overwhelming them with unnecessary noise.
The new role system shipped in early 2025 using a phased rollout - starting with low-risk, restricted roles (farm hands and map-only users) before expanding to all eleven.
Execution
Though technical complexity extended delivery across multiple cycles, the extra time yielded a stable, thoroughly tested system.
Impact
The update significantly eased data confidentiality concerns for enterprise clients, directly smoothing sales conversations. Customer support tickets regarding access and permissions dropped immediately post-launch.
Future work
Advanced capabilities - edit/delete permissions by role, support-configured roles, and a custom role builder UI - remain deferred for future enterprise updates.